Post: AP, AME/ANE, AD(iCT)
- ☆1Operating SystemA computer has an Operating System (OS) installed on its SSD, and the SSD is detected in the BIOS. However, the computer boots from the network instead of the SSD. Which BIOS/UEFI setting should be changed to resolve this issue?BB, DEO, 26 | Data Entry OperatorChange the Boot Priority Order (Boot Sequence) to place the SSD first and disable PXE Network Boot if it is not needed.
Explanation: The computer boots from the device with the highest priority. Setting the SSD as the first boot device allows the installed OS to load instead of booting from the network.
Boot Priority Order (Boot Sequence) পরিবর্তন করে SSD-কে প্রথমে রাখতে হবে এবং প্রয়োজন না হলে PXE Network Boot বন্ধ করতে হবে।ব্যাখ্যা: কম্পিউটার Boot Priority অনুযায়ী প্রথম ডিভাইস থেকে চালু হওয়ার চেষ্টা করে। SSD-কে প্রথমে রাখলে Network-এর পরিবর্তে SSD-তে থাকা Operating System চালু হবে।
- ☆2Computer SecurityWhat is Two-Factor Authentication (2FA)? Define the CIA Triad.BB, DEO, 26 | Data Entry Operator
Two-Factor Authentication (2FA):
2FA is a security method that requires two different authentication factors to verify a user's identity before granting access.
Types of Authentication Factors:
1. Something You Know: Password or PIN.
2. Something You Have: Smartphone OTP or security token.
3. Something You Are: Fingerprint or facial recognition.CIA Triad:
The CIA Triad is a basic information security model consisting of three principles:
1. Confidentiality: Ensures that data is accessible only to authorized users.
2. Integrity: Ensures that data remains accurate, complete, and unaltered.
3. Availability: Ensures that systems and data are accessible to authorized users whenever needed.
Two-Factor Authentication (2FA):
2FA হলো একটি security পদ্ধতি, যেখানে কোনো user-এর পরিচয় যাচাই করে access দেওয়ার জন্য দুটি ভিন্ন authentication factor প্রয়োজন হয়।
Authentication Factor-এর ধরন:
১. Something You Know: Password বা PIN।
২. Something You Have: Smartphone OTP বা Security Token।
৩. Something You Are: Fingerprint বা Facial Recognition।CIA Triad:
CIA Triad হলো Information Security-এর একটি মৌলিক মডেল, যা তিনটি নীতির সমন্বয়ে গঠিত:
১. Confidentiality: নিশ্চিত করে যে শুধু অনুমোদিত user-রা data access করতে পারবে।
২. Integrity: নিশ্চিত করে যে data সঠিক, সম্পূর্ণ ও অপরিবর্তিত থাকে।
৩. Availability: নিশ্চিত করে যে প্রয়োজনের সময় অনুমোদিত user-রা system ও data ব্যবহার করতে পারবে।
- ☆3Web TechnologyIdentify and explain the three main components of the following URL:
https://www.bb.org.bd/index.phpBB, DEO, 26 | Data Entry OperatorThree Main Components of a URL
Given URL: https://www.bb.org.bd/index.php
1. Protocol (Scheme): https://
It defines the communication protocol used to transfer data securely between the browser and the web server.2. Domain Name (Host): www.bb.org.bd
It is the human-readable address of the web server. Here, it refers to the Bangladesh Bank website.3. File Path (Resource): /index.php
It identifies the requested resource on the server, such as the PHP script used to generate a webpage.
URL-এর তিনটি প্রধান উপাদান
প্রদত্ত URL: https://www.bb.org.bd/index.php
১. Protocol (Scheme): https://
এটি Browser ও Web Server-এর মধ্যে নিরাপদে Data আদান-প্রদানের Communication Protocol নির্ধারণ করে।২. Domain Name (Host): www.bb.org.bd
এটি Web Server-এর সহজে পড়া যায় এমন ঠিকানা। এখানে এটি Bangladesh Bank-এর Website নির্দেশ করে।৩. File Path (Resource): /index.php
এটি Server-এ অনুরোধ করা Resource নির্দেশ করে, যেমন Webpage তৈরির জন্য ব্যবহৃত PHP Script।
- ☆4Microprocessor & Computer ArchitectureA computer's RAM has been upgraded from 8 GB to 16 GB, and its SSD capacity has been increased from 256 GB to 512 GB. Which upgrade allows the computer to run more applications simultaneously, and which upgrade allows it to store more data?BB, DEO, 26 | Data Entry Operator
1. More Simultaneous Applications: RAM Upgrade (8 GB to 16 GB)
RAM stores the data and instructions of running applications. Increasing RAM allows more applications to run simultaneously and smoothly.2. More Data Storage: SSD Upgrade (256 GB to 512 GB)
SSD provides permanent storage for the Operating System, software, documents, and other files. Increasing SSD capacity allows more data to be stored.
১. একসঙ্গে বেশি Application চালানো: RAM Upgrade (8 GB থেকে 16 GB)
RAM চলমান Application-এর Data ও Instruction সংরক্ষণ করে। RAM বাড়ালে একসঙ্গে বেশি Application চালানো যায় এবং কাজের গতি মসৃণ থাকে।২. বেশি Data সংরক্ষণ: SSD Upgrade (256 GB থেকে 512 GB)
SSD-তে Operating System, Software, Document ও অন্যান্য File স্থায়ীভাবে সংরক্ষিত থাকে। SSD-এর Capacity বাড়ালে বেশি Data রাখা যায়।
- ☆5MiscellaneousAn email mailbox has a storage quota of 2 GB. The following storage is occupied:
- Sent Items: 350 MB
- Inbox: 1.25 GB
- Trash: 900 KB
- Drafts: 120 MB
- How much mailbox storage is remaining?
- What should the email recipient do to receive a 300 MB file?
BB, DEO, 26 | Data Entry Operator(a) Remaining Mailbox Storage:
Total Quota = 2 GB = 2,000 MB
Total Used = 350 + 1,250 + 0.9 + 120 = 1,720.9 MB
Remaining Storage = 2,000 − 1,720.9 = 279.1 MB
(b) To Receive a 300 MB File:
Required Space = 300 − 279.1 = 20.9 MB
The recipient should free up at least 20.9 MB of mailbox storage, preferably 21 MB, by deleting unnecessary emails and emptying Trash. Alternatively, the sender can share the file through Google Drive or OneDrive.
(ক) অবশিষ্ট Mailbox Storage:
মোট Quota = 2 GB = 2,000 MB
মোট ব্যবহৃত Storage = 350 + 1,250 + 0.9 + 120 = 1,720.9 MB
অবশিষ্ট Storage = 2,000 − 1,720.9 = 279.1 MB
(খ) 300 MB File গ্রহণ করার উপায়:
অতিরিক্ত প্রয়োজনীয় Storage = 300 − 279.1 = 20.9 MB
প্রাপককে অপ্রয়োজনীয় Email মুছে অন্তত 20.9 MB, অর্থাৎ প্রায় 21 MB Storage খালি করতে হবে এবং Trash খালি করতে হবে। বিকল্পভাবে, প্রেরক Google Drive বা OneDrive-এর মাধ্যমে File-এর Link শেয়ার করতে পারেন।
- ☆6MiscellaneousDiscuss five advantages and five challenges of mobile banking.BB, DEO, 26 | Data Entry Operator
Advantages of Mobile Banking:
1. 24/7 Accessibility: Allows transactions anytime and anywhere without visiting a bank.
2. Financial Inclusion: Provides banking services to rural and unbanked people.
3. Time and Cost Efficiency: Saves time, travel costs, and transaction expenses.
4. Instant Transactions: Enables quick fund transfers and bill payments.
5. Automated Tracking: SMS alerts and digital statements help monitor transactions and expenses.
Challenges of Mobile Banking:
1. Security and Fraud Risks: Users may face phishing, SIM swapping, malware, and credential theft.
2. Network Infrastructure: Poor internet or mobile network coverage can interrupt services.
3. Digital Illiteracy: Some users struggle to operate mobile banking applications safely.
4. Device Dependency: Services depend on a functioning mobile device and sufficient battery power.
5. System Downtime and Limits: Server outages and transaction limits may delay payments or transfers.
Mobile Banking-এর সুবিধা:
১. ২৪/৭ ব্যবহার: ব্যাংকে না গিয়ে যেকোনো সময় ও স্থান থেকে লেনদেন করা যায়।
২. Financial Inclusion: গ্রামীণ ও ব্যাংকিং সেবার বাইরে থাকা মানুষকে ব্যাংকিং সেবার আওতায় আনে।
৩. সময় ও খরচ সাশ্রয়: সময়, যাতায়াত খরচ এবং লেনদেনের ব্যয় কমায়।
৪. তাৎক্ষণিক লেনদেন: দ্রুত অর্থ স্থানান্তর ও বিল পরিশোধ করা যায়।
৫. স্বয়ংক্রিয় হিসাব পর্যবেক্ষণ: SMS Alert ও Digital Statement-এর মাধ্যমে লেনদেন ও খরচ পর্যবেক্ষণ করা যায়।
Mobile Banking-এর চ্যালেঞ্জ:
১. Security ও Fraud Risk: Phishing, SIM Swapping, Malware এবং তথ্য চুরির ঝুঁকি থাকে।
২. Network Infrastructure: দুর্বল Internet বা Mobile Network-এর কারণে সেবা ব্যাহত হতে পারে।
৩. Digital Illiteracy: কিছু ব্যবহারকারী নিরাপদে Mobile Banking App ব্যবহার করতে সমস্যায় পড়েন।
৪. Device Dependency: সেবা ব্যবহারের জন্য সচল Mobile Device ও পর্যাপ্ত Battery প্রয়োজন।
৫. System Downtime ও Transaction Limit: Server বন্ধ থাকা বা লেনদেনের সীমার কারণে অর্থ স্থানান্তরে বিলম্ব হতে পারে।
- ☆7Computer SecurityExplain three fundamental principles of information security.BB, DEO, 26 | Data Entry Operator
Three Fundamental Principles of Information Security:
1. Principle of Least Privilege (PoLP): Users and applications should receive only the minimum access permissions necessary to perform their tasks. This reduces the risk of unauthorized access and damage.
2. Defense in Depth: Multiple layers of security, such as firewalls, MFA, antivirus, and encryption, are used to protect systems. If one layer fails, other layers provide additional protection.
3. Non-Repudiation: Ensures that a person cannot deny an action or message they have performed or sent. Digital signatures and audit logs help establish proof.
Information Security-এর তিনটি মৌলিক নীতি:
১. Principle of Least Privilege (PoLP): User ও Application-কে কাজের জন্য যতটুকু Access Permission প্রয়োজন, শুধু ততটুকুই দিতে হবে। এতে অননুমোদিত Access ও ক্ষতির ঝুঁকি কমে।
২. Defense in Depth: System সুরক্ষার জন্য Firewall, MFA, Antivirus ও Encryption-এর মতো একাধিক Security Layer ব্যবহার করা হয়। একটি Layer ব্যর্থ হলেও অন্য Layer সুরক্ষা প্রদান করে।
৩. Non-Repudiation: নিশ্চিত করে যে কোনো ব্যক্তি তার সম্পাদিত কাজ বা পাঠানো Message অস্বীকার করতে না পারে। Digital Signature ও Audit Log প্রমাণ হিসেবে কাজ করে।
- ☆8Programming ConceptGiven two integers A and B as input write a program to compute the least common multiple of A and B.BB, AP, 23 | Assistant Programmer
#include <stdio.h> int main () { int n1, n2, max; printf ("Enter two positive integers: "); scanf ("%d %d", &n1, &n2); // maximum number between n1 and n2 is stored in max max = (n1> n2) ? n1: n2; while (1) { // Check if max is divisible by both n1 and n2 if ((max% n1 == 0)&& (max % n2 ==0)) { // If true, max is the LCM of n1 and n2 printf("The LCM of %d and %d is %d.", n1,n2,max); break; } ++max; } return 0; }
Sample I/O: Enter two positive integers: 14 8 The LCM of 14 and 8 is 56. === Code Execution Successful ===🔗 Run Online: LCM of two integer
- ☆9Programming ConceptConsider the following code:
Public class Class A {
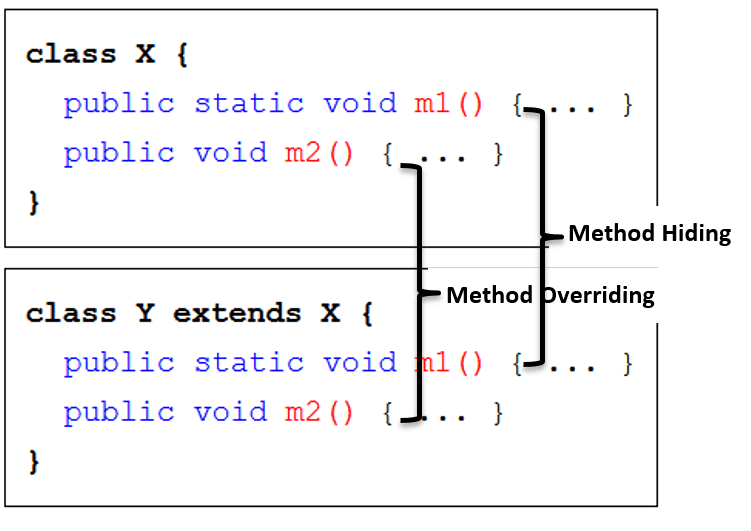
Mention which of the methods overload, override and hied supper class methods. What about the remaining method?
Public void m1 () {}
Public void m2 (int i) {}
Public void m3 (int i) {}
Public static void m4 (int i) {}
Public class class B extends class A {
Public static void ml (int i) {}
Public void m2 (int i) {}
Public void m3 (string s) {}
Public static void m4 (int i) {}BB, AP, 23 | Assistant Programmer
- ☆10Data StructureHeapConvert the array (56,33,48,29,99,12 and 344) into min heap.BB, AD(ICT), 25 | Bangladesh Bank
Initial array as a binary tree:
56 / \ 33 48 / \ / \ 29 99 12 344Swap 48 and 12:56 / \ 33 12 / \ / \ 29 99 48 344Swap 33 and 29:56 / \ 29 12 / \ / \ 33 99 48 344Swap 56 and 12:12 / \ 29 56 / \ / \ 33 99 48 344Swap 56 and 48:12 / \ 29 48 / \ / \ 33 99 56 344Final Result
The array now satisfies the min heap property: every parent node is smaller than or equal to its children.
12 / \ 29 48 / \ / \ 33 99 56 344 - ☆11Data StructureHeapGiven the adjacency list representation of a complete binary tree with 7 vertices, write the equivalent adjacency matrix representation. Assume that the vertices are numbered from 1 to 7 as in a binary heap.BB, AP, 23 | Assistant Programmer
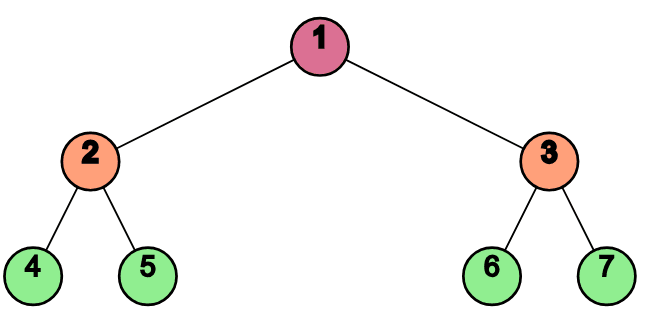
Complete Binary Tree
Adjacency List RepresentationVertex Connected Vertices 1 2, 3 2 4, 5 3 6, 7 4 5 6 7 Adjacency Matrix Representation
1 2 3 4 5 6 7 1 0 1 1 0 0 0 0 2 0 0 0 1 1 0 0 3 0 0 0 0 0 1 1 4 0 1 0 0 0 0 0 5 0 1 0 0 0 0 0 6 0 0 1 0 0 0 0 7 0 0 1 0 0 0 0
- ☆12Programming ConceptArrayWrite the pseudocode/ program (in any language) to print the common element between two arrays and the total number of such elements found. [assume each element in an array distinct].BB, AD(ICT), 25 | Bangladesh Bank
#include <iostream> using namespace std; int main() { int size1, size2; // Taking input size of first array cout << "Enter size of first array: "; cin >> size1; int arr1[size1]; cout << "Enter elements of first array:\n"; for (int i = 0; i < size1; i++) { cin >> arr1[i]; } // Taking input size of second array cout << "Enter size of second array: "; cin >> size2; int arr2[size2]; cout << "Enter elements of second array:\n"; for (int i = 0; i < size2; i++) { cin >> arr2[i]; } // To store common elements int commonElements[size1 < size2 ? size1 : size2]; int count = 0; // Check each element in arr1 against arr2 for (int i = 0; i < size1; i++) { bool found = false; for (int j = 0; j < size2; j++) { if (arr1[i] == arr2[j]) { found = true; break; } } if (found) { // Check for duplicates bool alreadyExists = false; for (int k = 0; k < count; k++) { if (commonElements[k] == arr1[i]) { alreadyExists = true; break; } } if (!alreadyExists) { commonElements[count] = arr1[i]; count++; } } } // Print common elements cout << "Common elements: "; for (int i = 0; i < count; i++) { cout << commonElements[i] << " "; } cout << endl; // Print total count cout << "Total number of common elements: " << count << endl; return 0; }Sample I/O: Enter size of first array: 5 Enter elements of first array: 0 20 30 40 50 Enter size of second array: 6 Enter elements of second array: 10 2 20 30 60 90 Common elements: 20 30 Total number of common elements: 2 === Code Execution Successful ===🔗 Run Online: Print Common Elements Between Two Arrays
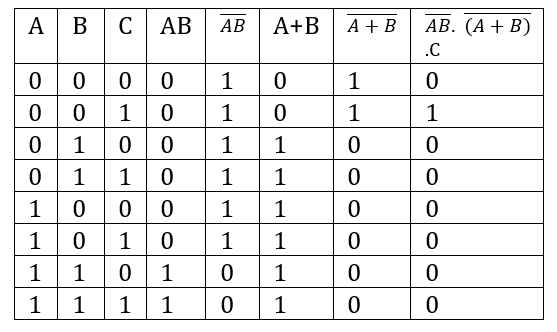
- ☆13Digital Logic DesignBasic GateGiven a logical function, find out the truth table of AB· (A+B).CBB, AD(ICT), 25 | Bangladesh Bank

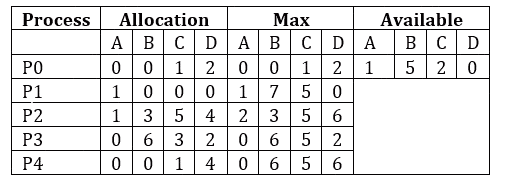
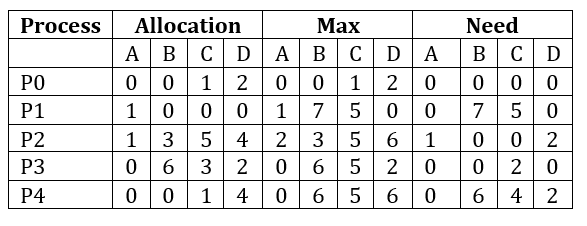
- ☆14Operating SystemDeadlockConsider the following snapshot of a system where maximum instance of A, B, C and D are 3, 14, 12 and 12.
Answer the following Question using the Bankers algorithm,
a) Calculate the need matrix from the above table?
b) Is the system in the safe state? Find out the safe sequence if no, justify the reason.BB, AD(ICT), 25 | Bangladesh Banka) answer:The Need matrix is calculated as: Need = Max - Allocation For each process, we subtract the Allocation from the Max to get the Need Matrix.

b) answer:Step-by-step checking for our system:
- P0: Needs [0, 0, 0, 0] ≤ Available [1, 5, 2, 0] → yes, so finish P0.
- Update Available by adding P0's allocation: [1, 5, 2, 0] + [0, 0, 1, 2] = [1, 5, 3, 2]
- P1: Needs [0, 7, 5, 0] ≤ Available [1, 5, 3, 2] → no, cannot finish yet.
- P2: Needs [1, 0, 0, 2] ≤ Available [1, 5, 3, 2] → yes, finish P2.
- Update Available : [1, 5, 3, 2] + [1, 3, 5, 4] = [2, 8, 8, 6]
- P3: Needs [0, 0, 2, 0] ≤ Available [2, 8, 8, 6] → yes, finish P3.
- Update Available : [2, 8, 8, 6] + [0, 6, 3, 2] = [2, 14, 11, 8]
- P4: Needs [0, 6, 4, 2] ≤ Available [2, 14, 11, 8] → yes, finish P4.
- Update Available : [2, 14, 11, 8] + [0, 0, 1, 4] = [2, 14, 12, 12]
- P1 (rechecked): Needs [0, 7, 5, 0] ≤ Available [2, 14, 12, 12] → yes, finish P1.
- Update Available : [2, 14, 12, 12] + [1, 0, 0, 0] = [3, 14, 12, 12]
Since all processes can finish in this order, the system is in a safe state.
Safe sequence: <P0, P2, P3, P4, P1>
🎥 Video Solution: Deadlock Handling (Deadlock Avoidance - Banker's Algorithm)
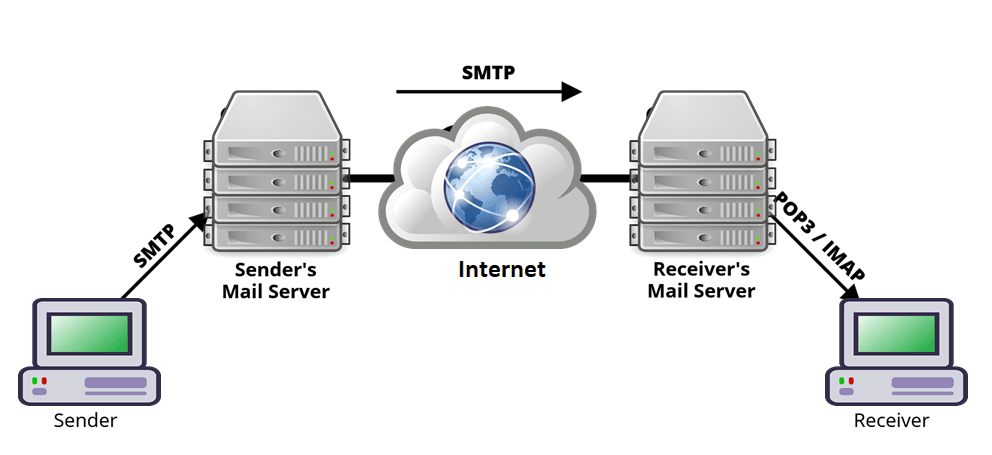
- ☆15Computer NetworkOSI/TCP-iPSynthia wants to send an email to her friend. He sends the email through the application and transport layer.
(a)Mention the protocol of application layer and transport layer
(b)Draw a diagram from the above scenario.BB, AD(ICT), 25 | Bangladesh BankProtocols used in Application Layer and Transport Layer:
Application Layer: The protocol commonly used here for sending emails is SMTP (Simple Mail Transfer Protocol).
Transport Layer: This layer is responsible for the reliable transmission of data between applications. The commonly used protocol at this layer is TCP (Transmission Control Protocol), which ensures that the data is delivered accurately and in order.
ব্যাখ্যা দেখুন:
Application Layer Protocol :Simple Mail Transfer Protocol(SMTP)
ইমেইল পাঠানোর জন্য Application Layer-এ SMTP ব্যবহৃত হয়। SMTP এর কাজ হলো একটি কম্পিউটার থেকে অন্য কম্পিউটারে ইমেইল মেসেজ পাঠানো। এটি ব্যবহারকারীকে সহজে ইমেইল লিখে পাঠানোর সুযোগ দেয় এবং সার্ভারগুলোর মধ্যে মেসেজ ট্রান্সফার পরিচালনা করে।
Transport Layer Protocol :TCP (Transmission Control Protocol)
Transport Layer-এর মূল কাজ হলো ডেটা নির্ভরযোগ্যভাবে (reliably) গন্তব্যে পৌঁছে দেওয়া।
TCP (Transmission Control Protocol) ব্যবহার করা হয় কারণ:
- এটি ডেটাকে ছোট ছোট অংশে (segments) ভেঙে পাঠায়।
- প্রতিটি অংশ ঠিকভাবে এবং সঠিক ক্রমে (in order) পৌঁছেছে কিনা তা যাচাই করে।
- ডেটা হারিয়ে গেলে পুনরায় পাঠানোর ব্যবস্থা করে।
ইমেইল একটি গুরুত্বপূর্ণ যোগাযোগ মাধ্যম। যদি মেসেজের কোনো অংশ হারিয়ে যায় বা এলোমেলোভাবে পৌঁছে যায়, তাহলে ইমেইলটি অপূর্ণ বা ভুল হয়ে যাবে। এজন্য Application Layer-এ SMTP ইমেইল পাঠানোর নিয়ম ঠিক করে দেয়, আর Transport Layer-এ TCP ডেটা সঠিকভাবে, সম্পূর্ণভাবে এবং নির্ভরযোগ্যভাবে পৌঁছানো নিশ্চিত করে।
(b) Answer:
The diagram illustrates the process of sending an email from the sender to the receiverব্যাখ্যা দেখুন:
Sender’s Device → Sender’s Mail Server এর সাথে SMTP protocol ব্যবহার করে যোগাযোগ করে।
Sender’s Mail Server → ইন্টারনেটের মাধ্যমে SMTP ব্যবহার করে ইমেইলটি Receiver’s Mail Server-এ পাঠায়।
Receiver’s Mail Server → ইমেইলটি Receiver’s Device-এ পৌঁছে দেওয়ার জন্য POP3 অথবা IMAP protocol ব্যবহার করে।
- ☆16Database Management SystemkeysFind the primary key and foreign key after decomposition of the given schema (Branch_name, Acc_name, Balance, Brnach_city, Assets) and then identify which normalization it is?BB, AD(ICT), 25 | Bangladesh Bank
Original Schema:
The original schema had attributes like Branch_name, Acc_name, Balance, Branch_city, and Assets.
Initially, everything was in a single table, but it had some issues because Branch_name was part of the key for identifying branch info, while Acc_no was the key for account info.
After Decomposition:
1. Account Table:
- Primary Key: Acc_no (Each account has a unique identifier).
- Foreign Key: Branch_name (This links each account to a branch).
- Non-key attributes (Acc_name, Balance) fully depend on Acc_no.
2. Branch Table:
- Primary Key: Branch_name (Each branch has a unique name).
- Non-key attributes (Branch_city, Assets) fully depend on Branch_name.
Why 2NF?
2NF (Second Normal Form) means:
- There are no partial dependencies (where attributes depend on part of the key).
- In each table, all non-key attributes depend entirely on the full primary key.
So, by breaking up the data into two tables, we've removed partial dependencies and made the schema 2NF.
Explanation:
১. প্রথমে একক টেবিলের স্কিমা:
আমাদের কাছে প্রথমে ছিল একটি টেবিল, এই টেবিলটির মধ্যে অ্যাট্রিবিউটগুলো হলো:
(Branch_name, Acc_name, Balance, Branch_city, Assets)
এই টেবিলটি ছিল একক টেবিল, কিন্তু এতে কিছু সমস্যা ছিল—বিশেষত partial dependency। এর মানে হলো, কিছু অ্যাট্রিবিউট (যেমন Branch_city এবং Assets) Branch_name এর উপর নির্ভরশীল, যেটি এই টেবিলের একটি অংশ। যাতে নরমালাইজেশন ছিলো না।
২. ডিকম্পোজিশন (Decomposition):
এখন, এই সমস্যা সমাধান করতে আমরা টেবিলটিকে দুটি আলাদা টেবিলে ভাগ করি:
Account Table:
(Account_no, Acc_name, Balance, Branch_name)
- Primary Key: Acc_noAcc_no একটি ইউনিক আইডেন্টিফায়ার, যা প্রতিটি অ্যাকাউন্টকে ইউনিক করে।
- Foreign Key: Branch_nameBranch_name একটি ফরেন কী হিসেবে কাজ করে, যা
Branchটেবিলের শাখার নামের সাথে সম্পর্কিত।
Branch Table:
- Primary Key: Branch_nameBranch_name শাখার ইউনিক আইডেন্টিফায়ার।
- Foreign Key: এখানে কোনো ফরেন কী নেই।
৩. ২NF (Second Normal Form):
Partial Dependency:
প্রথম স্কিমাতে Branch_name ছিল একটি অংশ, যা Branch_city এবং Assets এর মতো শাখার তথ্য ধারণ করছিল। তবে, অ্যাকাউন্টের জন্য প্রাথমিক কী Acc_no পুরোপুরি অ্যাকাউন্টের তথ্য (Acc_name, Balance) নির্ধারণ করতে ব্যবহৃত হয়।
ডিকম্পোজিশন করার পর, Account টেবিলের সমস্ত অ-প্রাথমিক অ্যাট্রিবিউট Acc_no এর উপর নির্ভরশীল হয়েছে, আর Branch টেবিলের সমস্ত অ-প্রাথমিক অ্যাট্রিবিউট Branch_name এর উপর নির্ভরশীল।
এটি partial dependency দূর করেছে, যেখানে কোনো অ্যাট্রিবিউট প্রাথমিক কীর একটি অংশের উপর নির্ভরশীল ছিল না।
২NF অর্জিত হয়েছে কারণ:
- Account টেবিলের সকল Non-key Attribute Acc_no এর উপর নির্ভরশীল।
- Branch টেবিলের সকল Non-key Attribute Branch_name এর উপর নির্ভরশীল
এই ডিকম্পোজিশনটি নিশ্চিত করেছে যে, আমরা partial dependency দূর করেছি এবং প্রতিটি টেবিলের Non-key Attribute তাদের পুরো primary keyএর উপর নির্ভরশীল। এর ফলে আমরা ২NF (Second Normal Form) অর্জন করেছি।
- ☆17Computer NetworkTransmission Mode and Network PerformanceSuppose Bangladesh bank is designing a nation of communication network for office located in Dhaka and Rangpur. Their offices are connected via wide area network (WAN). The team needs to ensure that applications with low latency requirements (such as VOIP and video conferencing) can operate efficiently between these offices. Given:
- Distance between Dhaka and Rangpur = 30 km
- Speed of fiber optic link = 2 × 10⁸ m/s
- Link capacity = 1 Gbps
- Average size of data packets = 15,000 bytes
- Delay at each router/switch along the path = 5 ms
- RTT between Dhaka and Rangpur = 50 ms
Calculate the total network latency between office at Dhaka and Rangpur, considering the propagation delay and transmission delay.BB, AD(ICT), 25 | Bangladesh Bank- Distance between Dhaka and Rangpur = 30 km = 30,000 meters
- Speed of fiber optic link = 2 × 10⁸ m/s
- Link capacity = 1 Gbps = 1 × 10⁹ bps
- Average size of data packets = 15,000 bytes = 120,000 bits (15,000 × 8)
- Delay at each router/switch = 5 ms
- RTT between Dhaka and Rangpur = 50 ms
Propagation Delay
Propagation Delay = Distance / Propagation Speed
= 30,000 meters / (2 × 10⁸ m/s) = 0.00015 seconds = 0.15 ms
Transmission Delay
Transmission Delay = Packet Size (bits) / Link Capacity (bps)
= 120,000 bits / (1 × 10⁹ bps) = 0.00012 seconds = 0.12 ms
Router Delay
There are 1 routers and 1 switch each with 5 ms delay:
Router Delay = 2 × 5 ms = 10 ms
Total One-Way Latency
Total Latency = Propagation Delay + Transmission Delay + Router Delay
= 0.15 ms + 0.12 ms + 10 ms = 10.27 ms (Answer)
Round Trip Time (RTT)
RTT = 2 × One-way latency (since round trip includes going and coming back)
RTT=2×10.27 ms=20.54 ms
The given RTT (50 ms) is higher, which suggests additional delays are present such as queuing delay, processing delay, or other network factors not explicitly included in the simple calculation.
🎥 Video Solution: Network Latency Calculation
🎥 Video Solution: Network Delay Types & Round-Trip Time Explained (in Bangla)
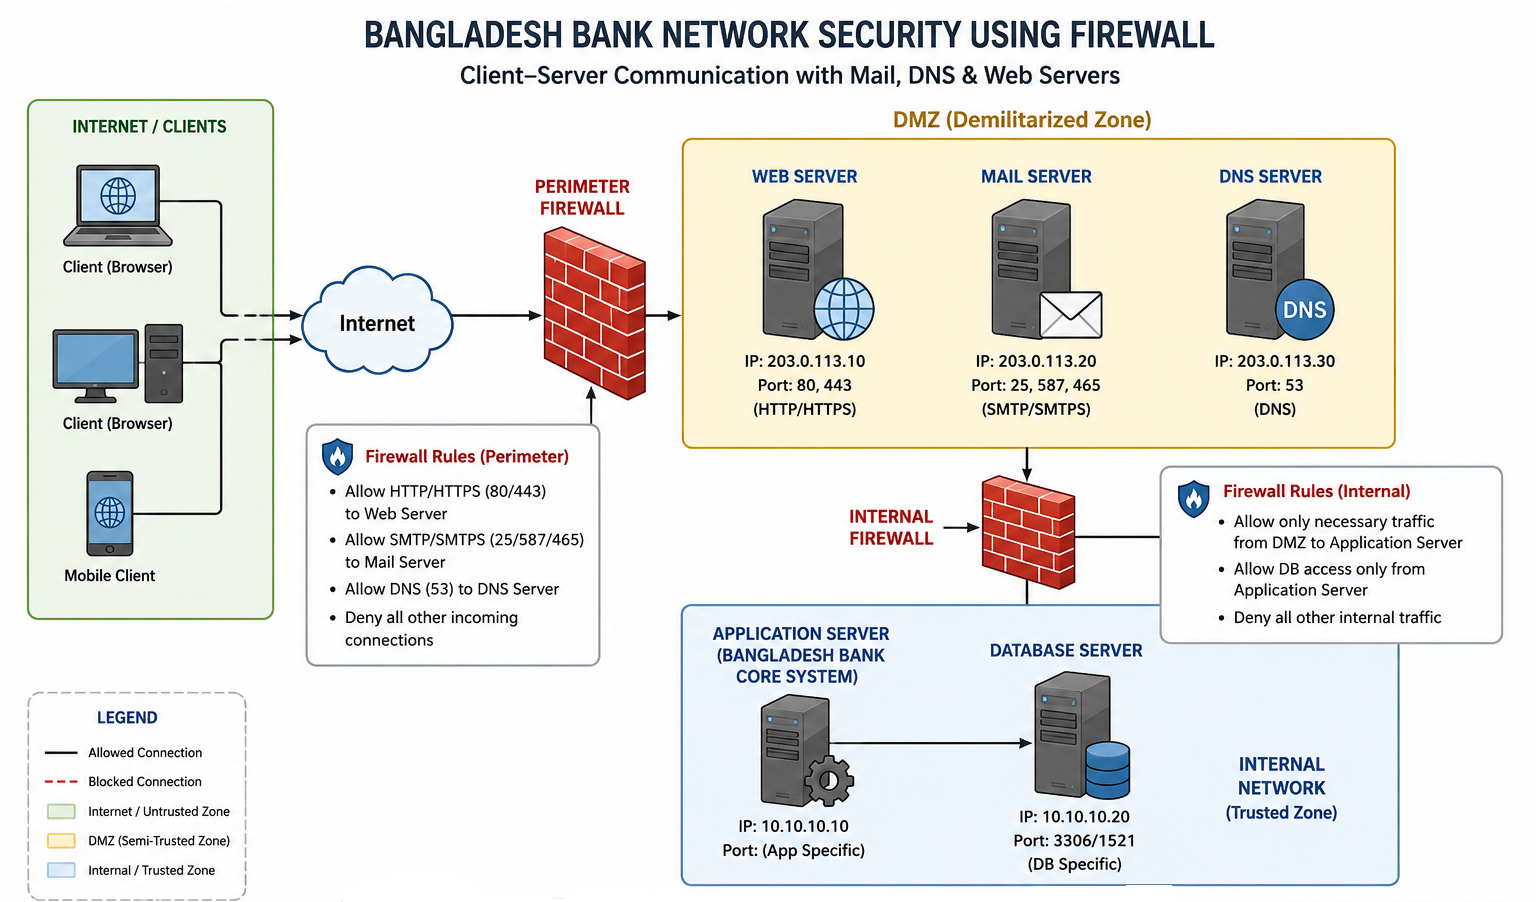
- ☆18Data Center & VirtualizationOthersBangladesh Bank have client server and the communicate with Mail server, DNS server, web server. Bangladesh Bank want to ensure the security using firewall on those server. Draw a diagram with the scenario.BB, AD(ICT), 25 | Bangladesh Bank
The diagram represents a secure network architecture for Bangladesh Bank, where client-server communication is protected using firewalls:The diagram illustrates a secure client-server architecture for Bangladesh Bank, where clients communicate with different servers through a firewall to ensure network security.
Clients (Users): Users access Bangladesh Bank's online services through the Internet using web browsers or mobile applications.
Perimeter Firewall: The first firewall acts as a security gateway between the Internet and the bank's servers. It filters incoming and outgoing traffic, allowing only authorized requests while blocking unauthorized access and cyber attacks.
DMZ (Demilitarized Zone): Public-facing servers are placed in the DMZ to minimize the risk of exposing the internal network. These include:
Web Server – Handles HTTP/HTTPS requests from clients.
Mail Server – Provides email services using SMTP/SMTPS protocols.
DNS Server – Resolves domain names to IP addresses for client requests.
Internal Firewall: A second firewall separates the DMZ from the bank's internal network. It allows only necessary communication between the public servers and the internal systems, preventing attackers from directly accessing sensitive resources.
Application Server: This server hosts Bangladesh Bank's core banking applications and business logic. It processes requests received from the Web Server and communicates with the Database Server.
Database Server: Stores confidential banking information such as customer records, transaction data, and account details. It is accessible only by the Application Server and is never exposed directly to the Internet.
Security Features
Filters unauthorized network traffic.
Allows only required ports and services (HTTP/HTTPS, SMTP, DNS).
Protects internal servers from external attacks.
Isolates public-facing servers using a DMZ.
Restricts access to sensitive banking data through an Internal Firewall.
Enhances confidentiality, integrity, and availability of banking services.
Conclusion:
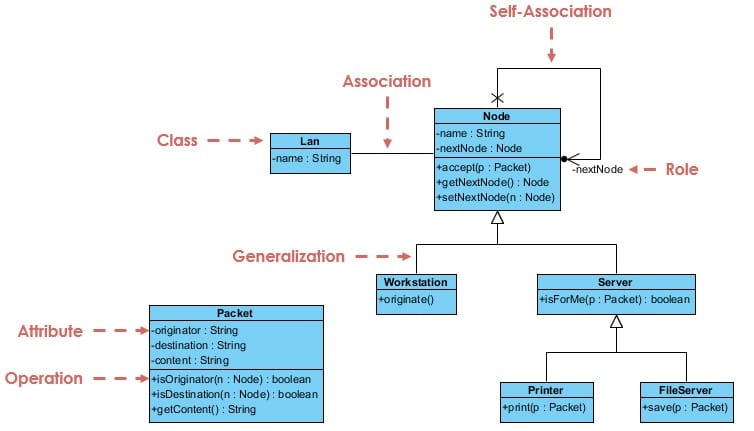
By deploying perimeter and internal firewalls along with a DMZ architecture, Bangladesh Bank ensures that client requests are securely processed while protecting its critical application and database servers from unauthorized access and cyber threats - ☆19Computer NetworkOthersDraw A class diagram. A token-ring based local area network (LAN) is a network consisting of nodes in which network packets are sent around. Every node has a unique name within the network, and refers to its next node. Different kinds of nodes exist: Workstations are originators of messages; servers and printers are network nodes that can receive messages. Packets contain an originator a destination and content, and are sent around on a network. A LAN is a circular configuration of nodes.BB, AP, 23 | Assistant Programmer
- ☆20Non Technical QuestionNon tech
∫ from 0 to 2 of (2x² + 3x) dx?
- In Bangladesh Bank there are 6 Assistant directors and 4 Deputy Directors (DD's). Each AD brings a bag, while only half of the DDs bring a bag. If a bag is selected at random from all the bags, what is the probability that the chosen bag belongs to a Deputy Director (DD)?
Translations:ক) শনিবার হতে সে অফিস আসছে না
খ) আপনার ব্যাংঙ্ক একাউন্টের স্থিতি জানার জন্য মোবাইল ব্যাংকিং এপ্লিকেশনে লগিন করুন- Short notes on "AI and machine language mitigate challenge of cyber attack on banking system"
BB, AD(ICT), 25 | Bangladesh Bank - ☆21Non Technical QuestionNon tech11. A father has divided his property between his two sons A and B. A invests the amount at a compound profit of 8% p.a. B invests the amount of 10% p.a. simple profit. At the end of 2 years, the profit received by B is Taka 1336 more than the interest received by A. Find A's share in the fathers property of Taka 25000.
12. The percentage profit earned by selling an artical for Tk. 1920 is equal to the percentage loss incurred by selling the same artical for Tk. 1280. At what price should the artical be sold to make 25% profit?
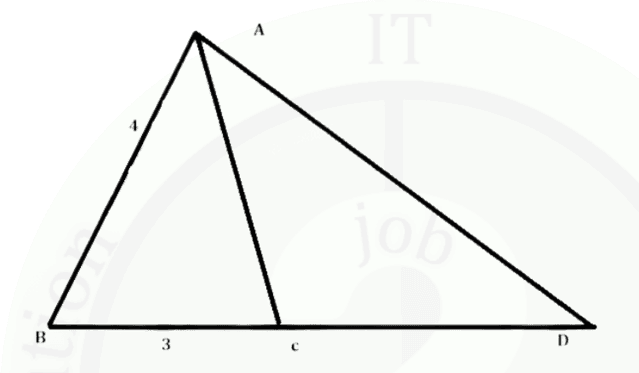
13. AD is the longest side of the triangle ABD shown in the figure, what is the length of longest side of ∆ABC?

14. $4 \frac{\sqrt{6} + \sqrt{2}}{\sqrt{6} - \sqrt{2}} - \frac{2 + \sqrt{3}}{2 - \sqrt{3}} = ?$BB, AME, 23 | AME/ANE/AE - ☆22Non Technical QuestionNon techGrowing use to technology in the Financial Service Industry.
11. Translation English to Bangla.
12. Translation Bangla to English.
13. If x is an Integer and x + 1/x= 17/4, then value of x – 1/x =?
14. A basketball team has won 15 games and lost 9. If these games represent 16% of the games to be played, then how many more games must the team win to average 75% for the season?
15. Students of a class are made to stand in rows. If 4 students are extra in each row, then there would be 2 rows less. If four students are less in each row, then there would be 4 more rows. What is the number of students in the class?
16. In the given figure, PQT is a right triangle then what is the area of square QRST.BB, AP, 23 | Assistant Programmer
- ☆23MCQMCQ
- Which the universal gate? Ans.: Nor and NAND gate
- What is best way to implement priority queue? Ans.: Heap
- Reverse voltage Zener diode is used as? Ans.: Voltage Regulator
- What kind of encryption is used for email? Ans.: TLS
- Which algorithm used digital signature? Ans.: RSA
- What is HTTP code 500? Ans.: Internal Server Error
- Which one make data access from a database faster? Ans.: Indexing
- Which device that's converts AC to DC? Ans.: Rectifier
- Priority scheduling math no arrival time, find the average TAT? Ans.: 0
- Find the current from a circuit, where voltage & resistance already given? Ans.: 0.5A
- What factors doesn’t affect inductance? Ans:
- What is the major drawback of waterfall model? Ans: lack of flexibility
- What is not a web server type? Ans:
- Docker containers within a single application?
- A circular queue has size 6, front 2nd index, rear 5th index. What will the position of rear after insert a value in front?
- During sending email that message should not alter/modify, which database properties ensure this?
- In binary tree what are the root value of the following 56, 58, 12, 78?
- Write the 2’s complement of (65)16.
- A process needs I/O operations, it switches to …..waiting state.
- Which the command of DDL?
- Integration testing is the process of testing the interface between two software or modules.
- SUEZ canal connects which two seas? Ans.: Mediterranean sea and the Red sea
- First ICC ODI Men's World Cup winner captain? Ans.: Clive Lloyd
- Who won the Nobel peace prize in 2024? Ans.: Nihon Hidankyo
- What the highest peak of Bangladesh? Ans.: Tazingdong
- Strasbourg belongs to which country? Ans.: France
- A pipe can fill a tank in 4 hours, and another pipe can fill it in 6 hours. How much time will they take to fill the tank together? Answer: 2.4 hours
- What is the distance from A's starting point to his final position? Answer: 4.24 meters
- Mr. X uses 30% of his salary for expenses, 20% for his final position, and 10% for another. His remaining amount is 12,000 Taka. What is his total salary? Ans.: 30,000
- The father's age is 36 and the son's age is 16. How many years ago was the father's age three times the son's age? Ans.: 6 years ago
- There are 8 balls, and one ball is heavier than the other 7, which are of the same weight. How many weighing are required to guarantee finding the heavier ball? Ans: 2
- 192.168.16.10, which the subnet address of this ip address?
- Find the output.
int main() { int x=3; int y=2; if (x==2) y=3; else y=2; printf("%d %d\n", x, y); }Ans.: 2, 3
BB, AD(ICT), 25 | Bangladesh Bank
- ☆24Data Structure_mathMath-HeapConvert the array (56,33,48,29,99,12 and 344) into min heap.BB, AD(ICT), 25_math | IT Mathematical Question
Initial array as a binary tree:
56 / \ 33 48 / \ / \ 29 99 12 344Swap 48 and 12:56 / \ 33 12 / \ / \ 29 99 48 344Swap 33 and 29:56 / \ 29 12 / \ / \ 33 99 48 344Swap 56 and 12:12 / \ 29 56 / \ / \ 33 99 48 344Swap 56 and 48:12 / \ 29 48 / \ / \ 33 99 56 344Final Result
The array now satisfies the min heap property: every parent node is smaller than or equal to its children.
12 / \ 29 48 / \ / \ 33 99 56 344
- ☆25Operating System_mathMath-Deadlock MathConsider the following snapshot of a system where maximum instance of A, B, C and D are 3, 14, 12 and 12.
Answer the following Question using the Bankers algorithm,
a) Calculate the need matrix from the above table?
b) Is the system in the safe state? Find out the safe sequence if no, justify the reason.BB, AD(ICT), 25_math | IT Mathematical Questiona) answer:The Need matrix is calculated as: Need = Max - Allocation For each process, we subtract the Allocation from the Max to get the Need Matrix.

b) answer:Step-by-step checking for our system:
- P0: Needs [0, 0, 0, 0] ≤ Available [1, 5, 2, 0] → yes, so finish P0.
- Update Available by adding P0's allocation: [1, 5, 2, 0] + [0, 0, 1, 2] = [1, 5, 3, 2]
- P1: Needs [0, 7, 5, 0] ≤ Available [1, 5, 3, 2] → no, cannot finish yet.
- P2: Needs [1, 0, 0, 2] ≤ Available [1, 5, 3, 2] → yes, finish P2.
- Update Available : [1, 5, 3, 2] + [1, 3, 5, 4] = [2, 8, 8, 6]
- P3: Needs [0, 0, 2, 0] ≤ Available [2, 8, 8, 6] → yes, finish P3.
- Update Available : [2, 8, 8, 6] + [0, 6, 3, 2] = [2, 14, 11, 8]
- P4: Needs [0, 6, 4, 2] ≤ Available [2, 14, 11, 8] → yes, finish P4.
- Update Available : [2, 14, 11, 8] + [0, 0, 1, 4] = [2, 14, 12, 12]
- P1 (rechecked): Needs [0, 7, 5, 0] ≤ Available [2, 14, 12, 12] → yes, finish P1.
- Update Available : [2, 14, 12, 12] + [1, 0, 0, 0] = [3, 14, 12, 12]
Since all processes can finish in this order, the system is in a safe state.
Safe sequence: <P0, P2, P3, P4, P1>
🎥 Video Solution: Deadlock Handling (Deadlock Avoidance - Banker's Algorithm)
- ☆26Microprocessor & Computer ArchitectureCachingSuppose we have a 16 KB of data in a direct mapped cache with 4 word blocks. Determine the size of the tag, index and offset fields if we are using a 32-bit architecture.BB, AME, 23 | AME/ANE/AE
In direct mapping physical address is divided into three parts i.e., Tag bits, Cache Line Number and Byte offset.
Tag Number of Cache Lines/Index bit Offset Bit Given:-
Cache size: 16 KB
Block size: 4 words
Word size: 4 bytes (assuming a typical 32-bit architecture where each word is 4 bytes)
Address size: 32 bits
Calculate the Block Size in Bytes:
Since each block contains 4 words and each word is 4 bytes:
Block size = \( 4 \text{ words} \times 4 \text{ bytes/word} = 16 = 2^4 \text{ bytes} \)
Number of offset bits = \( \log_2 2^4 \) = 4 bits
Calculate the Number of Cache Blocks:
Block size = Line size = \( 2^4 \text{ bytes} \)
The total cache size is 16 KB = \( 2^{14} \text{ bytes} \) [ 1 KB = 210B]
Number of Lines = \( \frac{\text{Total cache size}}{\text{Line size}} = \frac{2^{14}}{2^4} = 2^{10} \text{ lines} \)
Number of Lines in the cache:
Number of index bits = \( \log_2 \text{(Number of lines)} = \log_2 2^{10} = \) 10 bits
Number of tag bits = Total Address bit − (Index bits + Offset bits) = \( 32 – (10 + 4) = \) 18 bits.
- ☆27Data CommunicationError DetectionExplain parity method for error detection. Write down the bit strings of "Delta" using ASCII.BB, AME, 23 | AME/ANE/AE
Parity Bit and Error Detection
During data transmission, electrical noise may change the logic level of a signal, causing errors. To detect such errors, a parity bit (an extra bit 0 or 1) is added to the original data.
Even Parity Method: The sender counts the number of 1s in the data. If the count is odd, the parity bit is set to 1 to make the total number of 1s even. If the count is already even, the parity bit is set to 0. The receiver again counts the number of 1s (including the parity bit). If the total is even, the data is assumed correct; otherwise, an error is detected.
Example: Suppose the data 1101 is transmitted with parity bit 1. If due to noise the receiver gets 1111, the total number of 1s becomes odd. Hence, the receiver detects an error and may request retransmission.
ASCII Code for “Delta”
Character Decimal ASCII 8-bit Binary D 68 01000100 e 101 01100101 l 108 01101100 t 116 01110100 a 97 01100001 The complete binary bit stream for “Delta” is:
01000100 01100101 01101100 01110100 01100001Parity Bit এবং Error Detection
Data transmission-এর সময় electrical noise signal-এর logic level পরিবর্তন করতে পারে, ফলে error তৈরি হয়। এই error শনাক্ত করার জন্য মূল data-এর সাথে একটি অতিরিক্ত bit যোগ করা হয়, যাকে parity bit বলা হয়।
Even Parity পদ্ধতি: Sender data-এর মধ্যে কতগুলো 1 আছে তা গণনা করে। যদি 1-এর সংখ্যা odd হয়, তাহলে parity bit = 1 দেওয়া হয় যাতে মোট সংখ্যা even হয়। Receiver আবার parity bit সহ 1-এর সংখ্যা গণনা করে। যদি মোট সংখ্যা even হয়, data সঠিক ধরা হয়; নাহলে error ধরা পড়ে।
উদাহরণ: ধরা যাক 1101 data parity bit 1 সহ পাঠানো হলো। Noise-এর কারণে receiver যদি 1111 পায়, তাহলে মোট 1-এর সংখ্যা odd হবে। তাই receiver বুঝবে যে error হয়েছে।
“Delta” শব্দের ASCII Code
Character Decimal ASCII 8-bit Binary D 68 01000100 e 101 01100101 l 108 01101100 t 116 01110100 a 97 01100001 “Delta”-এর সম্পূর্ণ binary bit string হলো:
01000100 01100101 01101100 01110100 01100001
- ☆28MiscellaneousothersSuppose that a digitized TV picture is to be transmitted from a source that uses a matrix of 480 × 500 picture elements (pixels), where each pixel can take on one of 32 intensity values. Assume that 30 pictures are sent per second. (This digital source is roughly equivalent to broadcast TV standards that have been adopted.) Find the source rate R (bps).BB, AME, 23 | AME/ANE/AE
Solution: Here, The source uses 480 x 500 pixels/picture And, 30 pictures are sent per second.
So, we can find the source rate in pixels/s as: \[ (30 \, \text{pictures/s}) \times (480 \times 500 \, \text{pixels/picture})\] \[= 7.2 \times 10^6 \, \text{pixels/s} \]
Now, each pixel can take on one of 32 intensity values and these 32 intensity values can be represented by: \[ \log_2 32 = \log_2 2^5 = 5 \, \text{bits} \] We can find the source rate in bits/s (bps) as:
R = \( 7.2 \times 10^6 \, \text{pixels/s} \times 5 \, \text{bits/pixel} \) \[ = 36 \times 10^6 \, \text{bps} = 36 \, \text{Mbps} \]
source:[brainly.in]
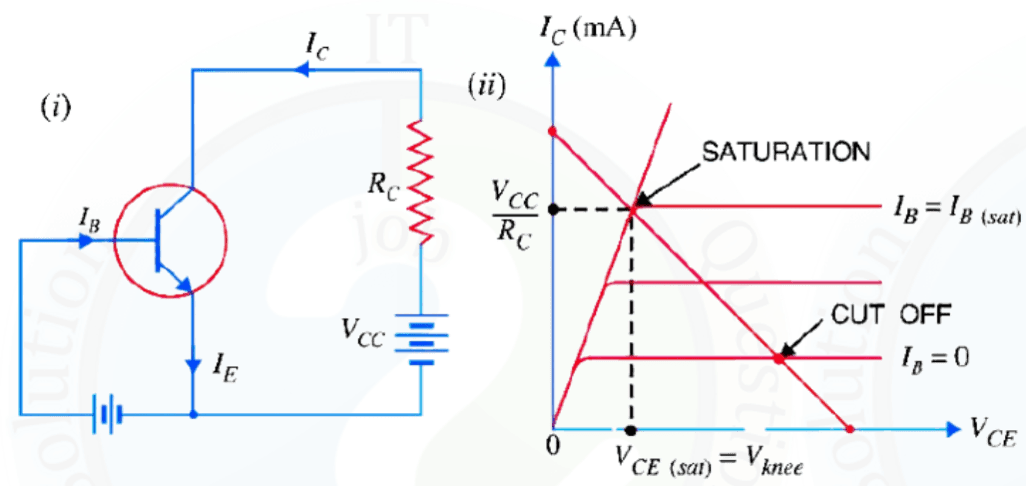
- ☆29MiscellaneousothersDescribe cut off, saturation and active region of operation of a transistor with diagram. Explain the working principle of an n-channel JFET with various values of VGS and VDS.BB, AME, 23 | AME/ANE/AE

Regions of Operation of a Transistor
A transistor operates in three main regions based on the biasing of its junctions: Cut-off region, Active region, and Saturation region. These regions are explained below with reference to the load line diagram.
(i) Cut-off Region
The cut-off region is the point where the load line intersects the curve for IB = 0. In this region, the base current is zero, and only a very small collector leakage current (ICEO) flows.
- Base-emitter junction is not forward biased.
- Collector-base junction is reverse biased.
- Transistor is in OFF state.
- Collector-emitter voltage is maximum: VCE ≈ VCC.
(ii) Saturation Region
The saturation region occurs where the load line intersects the curve for IB = IB(sat). In this region, both the base current and collector current are maximum.
- Base-emitter junction is forward biased.
- Collector-base junction is no longer reverse biased.
- Transistor is fully ON.
- Collector-emitter voltage is minimum: VCE(sat) ≈ 0.
(iii) Active Region
The active region lies between cut-off and saturation. In this region, the transistor operates normally and is used for amplification.
- Base-emitter junction is forward biased.
- Collector-base junction is reverse biased.
- Collector current is proportional to base current.
- Transistor works as an amplifier.

Working Principle of an N-Channel JFET
An N-channel Junction Field Effect Transistor (JFET) is a voltage-controlled semiconductor device where the current flows through an n-type channel between the Source and Drain. The current is controlled by the voltage applied between the Gate and Source (VGS).
Case 1: VGS = 0 and Small VDS
When no gate voltage is applied (VGS = 0) and a small drain-source voltage (VDS) is applied, electrons flow freely from source to drain. The channel is wide, and the drain current (ID) increases linearly with VDS. This region is called the ohmic or linear region.
Case 2: VGS = 0 and Increasing VDS
As VDS increases, the depletion region near the drain widens. At a particular VDS, the channel becomes constricted at the drain end. This condition is called pinch-off. Beyond this point, the drain current becomes almost constant. This is the saturation region.
Case 3: Negative VGS and Constant VDS
When a negative voltage is applied to the gate (VGS < 0), the depletion regions expand further, narrowing the channel. As a result, the drain current decreases. More negative VGS reduces ID further.
Case 4: VGS = VGS(off)
When VGS reaches a sufficiently negative value known as cut-off voltage (VGS(off)), the channel is completely closed. The drain current becomes zero, and the JFET is in the cut-off region.

Transistor-এর Operation-এর অঞ্চলসমূহ
Transistor-এর junction biasing-এর উপর ভিত্তি করে এটি তিনটি প্রধান region-এ কাজ করে: Cut-off region, Active region এবং Saturation region। Load line diagram-এর সাহায্যে এগুলো নিচে ব্যাখ্যা করা হলো।
(i) Cut-off Region
Cut-off region হলো সেই বিন্দু যেখানে load line, IB = 0 curve-কে ছেদ করে। এই অবস্থায় base current শূন্য থাকে এবং কেবলমাত্র অল্প collector leakage current (ICEO) প্রবাহিত হয়।
- Base-emitter junction forward biased থাকে না।
- Collector-base junction reverse biased থাকে।
- Transistor OFF অবস্থায় থাকে।
- Collector-emitter voltage সর্বাধিক: VCE ≈ VCC।
(ii) Saturation Region
Saturation region ঘটে যখন load line, IB = IB(sat) curve-কে ছেদ করে। এই অবস্থায় base current ও collector current উভয়ই সর্বাধিক হয়।
- Base-emitter junction forward biased থাকে।
- Collector-base junction reverse biased থাকে না।
- Transistor সম্পূর্ণ ON অবস্থায় থাকে।
- Collector-emitter voltage খুব কম: VCE(sat) ≈ 0।
(iii) Active Region
Cut-off ও saturation-এর মধ্যবর্তী অঞ্চলকে active region বলা হয়। এই অঞ্চলে transistor স্বাভাবিকভাবে কাজ করে এবং amplification-এর জন্য ব্যবহৃত হয়।
- Base-emitter junction forward biased থাকে।
- Collector-base junction reverse biased থাকে।
- Collector current, base current-এর সাথে proportional হয়।
- Transistor amplifier হিসেবে কাজ করে।

N-Channel JFET-এর কার্যপ্রণালী
N-channel Junction Field Effect Transistor (JFET) হলো একটি voltage-controlled device যেখানে Source এবং Drain-এর মধ্যে n-type channel দিয়ে current প্রবাহিত হয়। Gate এবং Source-এর মধ্যে প্রয়োগকৃত ভোল্টেজ (VGS) দ্বারা এই current নিয়ন্ত্রিত হয়।
কেস ১: VGS = 0 এবং ছোট VDS
যখন gate-এ কোনো voltage দেওয়া হয় না (VGS = 0) এবং drain-source-এর মধ্যে অল্প VDS প্রয়োগ করা হয়, তখন electron সহজে source থেকে drain-এ প্রবাহিত হয়। Channel প্রশস্ত থাকে এবং ID ধীরে ধীরে বাড়ে। একে ohmic বা linear region বলা হয়।
কেস ২: VGS = 0 এবং VDS বাড়ানো হলে
VDS বাড়ার সাথে সাথে drain-এর কাছে depletion region প্রসারিত হয়। একটি নির্দিষ্ট VDS-এ channel সংকুচিত হয়ে যায়, যাকে pinch-off বলা হয়। এর পর drain current প্রায় ধ্রুব থাকে। এটি saturation region।
কেস ৩: Negative VGS এবং স্থির VDS
Gate-এ negative voltage দিলে (VGS < 0), depletion region আরও বাড়ে এবং channel সরু হয়ে যায়। ফলে drain current কমে যায়। VGS যত বেশি negative হবে, ID তত কমবে।
কেস ৪: VGS = VGS(off)
যখন VGS একটি নির্দিষ্ট negative মানে পৌঁছে যায়, যাকে cut-off voltage (VGS(off)) বলা হয়, তখন channel সম্পূর্ণ বন্ধ হয়ে যায়। Drain current শূন্য হয় এবং JFET cut-off region-এ চলে যায়।
- ☆30Computer NetworkPacketization delayOne of the drawbacks of a small packet size is that a large fraction of link bandwidth is consumed by overhead bytes. To this end, suppose that the packet consists of P bytes and 5 bytes of header. Consider sending a digitally encoded voice source directly. Suppose the source is encoded at a constant rate of 128 kbps. Assume each packet is entirely filled before the source sends the packet into the network. The time required to fill a packet is the packetization delay. Determine the packetization delay for length L = 1500 bytes (roughly corresponding to maximum-sized Ethernet packet).BB, AME, 23 | AME/ANE/AE
Determine the Payload Size
The payload size is the part of a packet that excludes the header.
Payload Size = Total Packet Size − Header Size
Given:
Total Packet Size = 1500 bytes
Header Size = 5 bytesPayload Size = 1500 − 5 = 1495 bytes
Convert Payload Size to Bits
Since data rate is given in bits per second, payload size must be converted to bits.
Payload Size (bits) = 1495 × 8 = 11,960 bits
Calculate Packetization Delay
Packetization delay is the time needed to fill a packet with data.
Packetization Delay = Packet Length (bits) / Source Data Rate
Packet Length = 12,000 bits
Source Data Rate = 128,000 bpsPacketization Delay = 12,000 / 128,000 = 0.09375 s = 93.75 ms
Calculate Transmission Time
Transmission time is the time required to send the payload over the network.
Transmission Time = Payload Size (bits) / Data Rate
Transmission Time = 11,960 / 128,000 = 0.0934375 s = 93.4375 ms
- Payload Size: 11,960 bits
- Packetization Delay: 93.75 milliseconds
- Transmission Time: 93.4375 milliseconds
Payload Size নির্ধারণ
Payload size হলো packet-এর সেই অংশ যেখানে header বাদ দেওয়া হয়।
Payload Size = Total Packet Size − Header Size
প্রদত্ত:
Total Packet Size = 1500 bytes
Header Size = 5 bytesPayload Size = 1500 − 5 = 1495 bytes
Payload Size কে Bits-এ রূপান্তর
Data rate bits per second-এ দেওয়া থাকায় payload size bits-এ রূপান্তর করতে হবে।
Payload Size (bits) = 1495 × 8 = 11,960 bits
Packetization Delay নির্ণয়
Packetization delay হলো packet পূর্ণ হতে যে সময় লাগে।
Packetization Delay = Packet Length (bits) / Source Data Rate
Packet Length = 12,000 bits
Source Data Rate = 128,000 bpsPacketization Delay = 12,000 / 128,000 = 0.09375 s = 93.75 ms
Transmission Time নির্ণয়
Transmission time হলো payload network দিয়ে পাঠাতে যে সময় লাগে।
Transmission Time = Payload Size (bits) / Data Rate
Transmission Time = 11,960 / 128,000 = 0.0934375 s = 93.4375 ms
- Payload Size: 11,960 bits
- Packetization Delay: 93.75 milliseconds
- Transmission Time: 93.4375 milliseconds
- ☆31Cloud ComputingBasicExplain IaaS, PaaS, and SaaS with respect to cloud computing.BB, AME, 23 | AME/ANE/AE
Infrastructure as a Service (IaaS)
IaaS provides the most basic level of cloud services by offering virtualized computing resources over the internet. Organizations can rent servers, storage, and networking resources on a pay-as-you-go basis, reducing the need for physical hardware.
Examples: Amazon Web Services (AWS EC2), Microsoft Azure Virtual Machines, Google Compute Engine (GCE)
Platform as a Service (PaaS)
PaaS provides a complete development platform that allows developers to build, deploy, and manage applications without managing the underlying infrastructure. It includes operating systems, databases, and development tools.
Examples: Google App Engine, Microsoft Azure App Service, Heroku
Software as a Service (SaaS)
SaaS delivers software applications over the internet. Users can access these applications through a web browser without installing or maintaining software locally.
Examples: Google Workspace, Microsoft 365, Salesforce
Infrastructure as a Service (IaaS)
IaaS হলো cloud computing-এর সবচেয়ে মৌলিক service model, যেখানে internet-এর মাধ্যমে virtualized computing resource প্রদান করা হয়। এতে server, storage ও networking ভাড়া নিয়ে ব্যবহার করা যায়।
Examples: Amazon Web Services (AWS EC2), Microsoft Azure Virtual Machines, Google Compute Engine (GCE)
Platform as a Service (PaaS)
PaaS এমন একটি platform সরবরাহ করে যার মাধ্যমে developer-রা infrastructure পরিচালনা না করেই application তৈরি, deploy ও manage করতে পারে। এতে operating system, database ও development tools অন্তর্ভুক্ত থাকে।
Examples: Google App Engine, Microsoft Azure App Service, Heroku
Software as a Service (SaaS)
SaaS হলো এমন একটি model যেখানে software application internet-এর মাধ্যমে ব্যবহারকারীদের কাছে সরবরাহ করা হয়। ব্যবহারকারীদের আলাদা করে software install করতে হয় না।
Examples: Google Workspace, Microsoft 365, Salesforce
- ☆32Data Center & VirtualizationBasicWhat are the challenges in optimizing energy efficiency of data centers? Explain!BB, AME, 23 | AME/ANE/AE
Challenges in Optimizing Energy Efficiency of Data Centers
Optimizing energy efficiency in data centers is critical but challenging due to several technical and operational factors.
- High Cooling Requirements: Servers generate a large amount of heat, requiring continuous cooling systems that consume significant energy.
- Underutilized Servers: Many servers run at low utilization but still consume near-maximum power.
- Growing Data Demand: Increasing data processing, cloud services, and AI workloads raise overall energy consumption.
- Power Distribution Loss: Energy losses occur during power conversion and distribution within the data center.
- Legacy Infrastructure: Older hardware and cooling systems are less energy-efficient.
- Complex Monitoring: Tracking and optimizing energy usage across thousands of components is difficult.
- Balancing Performance and Efficiency: Reducing energy use without affecting performance and availability is challenging.
Data Center-এর Energy Efficiency উন্নত করার চ্যালেঞ্জসমূহ
Data center-এ energy efficiency বাড়ানো গুরুত্বপূর্ণ হলেও এতে বিভিন্ন প্রযুক্তিগত ও পরিচালনাগত চ্যালেঞ্জ রয়েছে।
- উচ্চ Cooling প্রয়োজন: Server থেকে প্রচুর তাপ উৎপন্ন হয়, যা কমাতে সবসময় cooling system চালু রাখতে হয় এবং এতে অনেক বিদ্যুৎ খরচ হয়।
- Server Underutilization: অনেক server কম কাজ করলেও প্রায় সম্পূর্ণ বিদ্যুৎ ব্যবহার করে।
- Data Demand বৃদ্ধি: Cloud, AI ও data processing বৃদ্ধির ফলে energy ব্যবহার বেড়ে যায়।
- Power Loss: Power conversion ও distribution-এর সময় শক্তির অপচয় হয়।
- পুরনো Infrastructure: পুরনো hardware ও cooling system কম কার্যকর।
- Monitoring জটিলতা: হাজারো component-এর energy usage পর্যবেক্ষণ করা কঠিন।
- Performance বনাম Efficiency: Energy কমাতে গিয়ে performance ও availability বজায় রাখা কঠিন।
- ☆33Object Oriented ProgrammingBasicDetermine overloading method, overridden method and hide super class method?BB, AP, 23 | Assistant Programmer
Method Overloading, Method Overriding, and Method Hiding
1. Method Overloading
Method overloading occurs when multiple methods in the same class have the same method name but different parameter lists (different number, type, or order of parameters).
- Resolved at compile time
- Improves code readability and flexibility
Example:
int add(int a, int b) int add(int a, int b, int c)2. Method Overriding
Method overriding happens when a subclass provides a new implementation of a method that is already defined in its superclass with the same method signature.
- Occurs in inheritance
- Resolved at runtime (runtime polymorphism)
- Method must be non-static
Example:
class Parent { void show() { } } class Child extends Parent { void show() { } }3. Method Hiding (Hiding Superclass Method)
Method hiding occurs when a static method in a subclass has the same name and signature as a static method in the superclass.
- Applies only to static methods
- Resolved at compile time
- Not true overriding
Example:
class Parent { static void display() { } } class Child extends Parent { static void display() { } }Summary Comparison
- Overloading: Same class, same method name, different parameters
- Overriding: Subclass redefines superclass method (non-static)
- Hiding: Static method in subclass hides static method of superclass
Method Overloading, Method Overriding এবং Method Hiding
১. Method Overloading
একই class-এর ভেতরে একই নামের method থাকলে কিন্তু তাদের parameter আলাদা হলে তাকে method overloading বলে।
- Compile time-এ সিদ্ধান্ত হয়
- Code সহজ ও flexible হয়
উদাহরণ:
int add(int a, int b) int add(int a, int b, int c)২. Method Overriding
Subclass যখন superclass-এর একটি non-static method একই signature দিয়ে নতুনভাবে implement করে, তখন তাকে method overriding বলে।
- Inheritance-এর ক্ষেত্রে হয়
- Runtime-এ সিদ্ধান্ত হয়
উদাহরণ:
class Parent { void show() { } } class Child extends Parent { void show() { } }৩. Method Hiding (Superclass Method Hide করা)
Subclass যদি superclass-এর static method একই নাম ও signature দিয়ে define করে, তাহলে তাকে method hiding বলে।
- শুধু static method-এর ক্ষেত্রে হয়
- Compile time-এ resolve হয়
- এটা real overriding নয়
উদাহরণ:
class Parent { static void display() { } } class Child extends Parent { static void display() { } }সংক্ষেপে পার্থক্য
- Overloading: একই class, আলাদা parameter
- Overriding: Subclass superclass-এর method পরিবর্তন করে
- Hiding: Static method subclass দ্বারা hide হয়
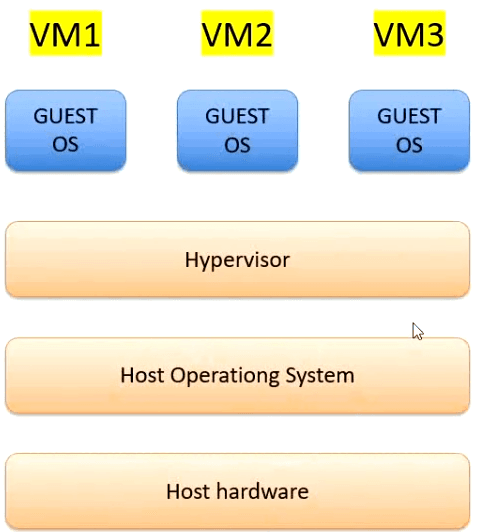
- ☆34Data Center & VirtualizationVMDefine a virtual machine with a neat diagram, explain the working of VM. What are the benefits of a VM?BB, AME, 23 | AME/ANE/AE
Virtual Machine:
A virtual machine (VM) is a software-based simulation of a physical computer. It runs an operating system and applications just like a physical computer.
Virtual Machine Operation:
=>VMs run on a physical host computer using a hypervisor (e.g., VMware, Hyper-V, VirtualBox)
=>A hypervisor, also known as a virtual machine monitor (VMM) or virtualizer, is a type of computer software, firmware or hardware that creates and runs virtual machines
=>The hypervisor allows multiple VMs to share the resources of a single physical host.
Benefits of Virtual Machines
Cost Efficiency: Reduced need for physical hardware.
Flexibility: Easy to test and deploy different operating systems and applications.
Resource Optimization: Better utilization of physical resources.
Disaster Recovery: Easier backup and restoration of VMs.
- ☆35Computer SecurityThreatsA bank has association with two different service providers as their payment gateways. The bank hires Mr. X to audit the payment gateway based on risk and threat detection. Which possible scenarios Mr. X will face?BB, AME, 23 | AME/ANE/AE
Possible Risk and Threat Scenarios Faced by Mr. X While Auditing Payment Gateways
While auditing two different payment gateway service providers for a bank, Mr. X may encounter the following risk and threat scenarios:
- Data Breach Risk: Sensitive customer data such as card numbers, CVV, or PINs may be exposed due to weak encryption or poor security controls.
- Man-in-the-Middle (MITM) Attacks: Attackers may intercept communication between the bank and the payment gateway if secure protocols (TLS/HTTPS) are misconfigured.
- Unauthorized Access: Weak authentication or improper access control may allow attackers or insiders to access payment systems.
- Malware and Trojan Attacks: Payment gateway servers may be infected with malware that captures transaction data.
- Fraudulent Transactions: Lack of proper monitoring and anomaly detection can lead to fake or unauthorized transactions.
- Compliance Risk: One or both gateways may not comply with standards such as PCI-DSS, increasing legal and financial risk.
- Availability Threats: Denial of Service (DoS/DDoS) attacks may disrupt payment services, affecting banking operations.
- Third-Party Dependency Risk: Security weakness in one service provider can impact the bank even if the bank’s internal systems are secure.
Conclusion: Mr. X must evaluate both technical and operational risks, compare security maturity levels of the two providers, and recommend mitigation strategies.
Payment Gateway Audit করার সময় Mr. X যে সম্ভাব্য Risk ও Threat-এর মুখোমুখি হতে পারেন
ব্যাংকের দুইটি ভিন্ন payment gateway service provider audit করার সময় Mr. X নিম্নলিখিত ঝুঁকি ও হুমকির সম্মুখীন হতে পারেন:
- Data Breach Risk: দুর্বল encryption বা security ব্যবস্থার কারণে card number, CVV বা PIN ফাঁস হতে পারে।
- Man-in-the-Middle (MITM) Attack: TLS/HTTPS সঠিকভাবে configure না থাকলে attacker bank ও gateway-এর মাঝখানে data intercept করতে পারে।
- Unauthorized Access: দুর্বল authentication বা access control থাকলে অননুমোদিত ব্যক্তি system access পেতে পারে।
- Malware ও Trojan Attack: Gateway server malware দ্বারা আক্রান্ত হয়ে transaction data চুরি হতে পারে।
- Fraudulent Transaction: Proper monitoring না থাকলে ভুয়া বা অননুমোদিত লেনদেন ঘটতে পারে।
- Compliance Risk: PCI-DSS-এর মতো security standard না মানলে আইনগত ও আর্থিক ঝুঁকি তৈরি হয়।
- Availability Threat: DoS বা DDoS attack-এর কারণে payment service বন্ধ হয়ে যেতে পারে।
- Third-Party Dependency Risk: Service provider-এর দুর্বলতা সরাসরি ব্যাংকের উপর প্রভাব ফেলতে পারে।
Mr. X-কে দুইটি provider-এর security posture তুলনা করে ঝুঁকি নির্ধারণ ও সমাধানের সুপারিশ করতে হবে।
- ☆36Computer SecurityThreatsDescribe a man-in the middle attack on the Diffie-Hellman key exchange protocol in which the adversary generates two public key pairs for the attack.BB, AP, 23 | Assistant Programmer
Man-in-the-Middle (MITM) Attack on Diffie–Hellman Key Exchange
In a MITM attack on Diffie–Hellman (DH), an attacker (Mallory) sits between Alice and Bob, intercepts their public keys, and replaces them with her own. Since basic DH provides no authentication, Alice and Bob cannot verify the real sender of the public key.
Normal DH (No Attack)
- Public parameters: prime p, generator g
- Alice selects private key a, sends public key A = ga mod p
- Bob selects private key b, sends public key B = gb mod p
- Shared key: K = gab mod p
MITM Attack (Attacker Generates Two Key Pairs)
Step 1: Interception
Mallory intercepts Alice’s public key A and Bob’s public key B.Step 2: Mallory Creates Two Private Keys
Mallory chooses two private keys: m1 (for Bob) and m2 (for Alice).Step 3: Mallory Generates Two Public Keys
Mallory computes:
M1 = gm1 mod p
M2 = gm2 mod pStep 4: Key Replacement (Fake Public Keys)
Mallory sends M1 to Bob pretending it is from Alice.
Mallory sends M2 to Alice pretending it is from Bob.Step 5: Two Different Shared Keys are Formed
- Alice computes: K1 = (M2)a mod p (Alice–Mallory key)
- Bob computes: K2 = (M1)b mod p (Bob–Mallory key)
- Mallory can compute both keys:
K1 = (A)m2 mod p and K2 = (B)m1 mod p
Result
- Alice and Bob do not share the same secret key.
- Mallory shares one key with Alice and another key with Bob.
- Mallory can read, modify, and re-encrypt messages between them.
Why It Works
Because basic Diffie–Hellman does not provide authentication, public keys can be replaced without detection.
Prevention
- Use Authenticated Diffie–Hellman
- Use Digital Signatures / Certificates (PKI)
- Use TLS (DHE/ECDHE + certificates)
Diffie–Hellman Key Exchange-এ Man-in-the-Middle (MITM) Attack
MITM attack-এ attacker (Mallory) Alice এবং Bob-এর মাঝখানে বসে public key গুলো intercept করে এবং নিজের public key বসিয়ে দেয়। Basic Diffie–Hellman-এ authentication নেই, তাই Alice/Bob বুঝতে পারে না public key আসলেই কার কাছ থেকে এসেছে。
Normal DH (Attack নেই)
- Public parameter: prime p, generator g
- Alice private key a নেয়, public key পাঠায় A = ga mod p
- Bob private key b নেয়, public key পাঠায় B = gb mod p
- Shared key: K = gab mod p
MITM Attack (Attacker দুইটি Key Pair তৈরি করে)
Step 1: Interception
Mallory Alice-এর public key A এবং Bob-এর public key B intercept করে।Step 2: Mallory দুইটি Private Key নেয়
Mallory দুইটি private key বেছে নেয়: m1 (Bob-এর জন্য) এবং m2 (Alice-এর জন্য)।Step 3: Mallory দুইটি Public Key তৈরি করে
Mallory হিসাব করে:
M1 = gm1 mod p
M2 = gm2 mod pStep 4: Public Key Replace করে
Mallory Bob-কে M1 পাঠায় (যেন Alice পাঠিয়েছে)।
Mallory Alice-কে M2 পাঠায় (যেন Bob পাঠিয়েছে)।Step 5: দুইটা আলাদা Shared Key তৈরি হয়
- Alice হিসাব করে: K1 = (M2)a mod p (Alice–Mallory key)
- Bob হিসাব করে: K2 = (M1)b mod p (Bob–Mallory key)
- Mallory দুইটাই বের করতে পারে:
K1 = (A)m2 mod p এবং K2 = (B)m1 mod p
Result
- Alice এবং Bob-এর মধ্যে একই secret key তৈরি হয় না।
- Mallory Alice-এর সাথে একটি key এবং Bob-এর সাথে আরেকটি key share করে।
- Mallory মাঝখান থেকে message পড়তে, পরিবর্তন করতে, এবং পুনরায় encrypt করে পাঠাতে পারে।
কেন Attack কাজ করে
Basic Diffie–Hellman-এ authentication নেই, তাই public key সহজে replace করা যায়।
Prevention
- Authenticated Diffie–Hellman ব্যবহার
- Digital Signature / Certificate (PKI) ব্যবহার
- TLS (DHE/ECDHE + certificate) ব্যবহার
- ☆37Software EngineeringTesting & QualityVerification and validation are two process areas at CMMI level 3. For both of these areas (a) provide a definition (b) a description of how you can fulfill these areas in your software testing activities.BB, AME, 23 | AME/ANE/AE
(a) Definition
Verification: Verification is the process of evaluating work products such as requirements, design, and code against predefined standards and specifications. It answers the question: “Are we building the product correctly?”
Validation: Validation focuses on evaluating the final product to ensure it meets user needs and expectations. It answers the question: “Are we building the right product?”
(b) Implementation of Verification and Validation in Software Testing
Verification Activities
Requirement Analysis: Functional and non-functional requirements are reviewed to identify testable requirements. A Requirement Traceability Matrix (RTM) is created to ensure each requirement is covered by test cases.
Test Planning and Documentation: A test plan is prepared defining scope, objectives, tools, and schedules to verify alignment with requirements.
Test Case Design and Development: Test cases are designed to verify individual components, including unit testing of modules.
Test Environment Setup: The test environment is configured to simulate real conditions, and smoke testing is performed.
Validation Activities
System Testing: The complete system is tested to validate overall functionality.
User Acceptance Testing (UAT): End users test the system to ensure it meets real-world requirements.
Performance and Usability Testing: Confirms system performance and user experience.
Test Execution and Bug Reporting: Test cases are executed, defects are logged, and fixes are retested.
Test Closure and Reporting: Test results are analyzed and documented, and lessons learned are discussed.
(ক) সংজ্ঞা
Verification: Verification হলো requirements, design ও code-এর মতো work product নির্দিষ্ট standard ও specification অনুযায়ী ঠিক আছে কিনা তা যাচাই করার প্রক্রিয়া। এটি প্রশ্নের উত্তর দেয়: “আমরা কি product ঠিকভাবে তৈরি করছি?”
Validation: Validation হলো চূড়ান্ত product ব্যবহারকারীর চাহিদা ও প্রত্যাশা পূরণ করছে কিনা তা নিশ্চিত করা। এটি প্রশ্নের উত্তর দেয়: “আমরা কি সঠিক product তৈরি করছি?”
(খ) Software Testing-এ Verification এবং Validation বাস্তবায়ন
Verification কার্যক্রম
Requirement Analysis: Functional ও non-functional requirement বিশ্লেষণ করে testable requirement নির্ধারণ করা হয় এবং RTM তৈরি করা হয়।
Test Planning ও Documentation: Scope, objective, tool ও schedule নির্ধারণ করে test plan তৈরি করা হয়।
Test Case Design ও Development: প্রতিটি module যাচাইয়ের জন্য test case ও unit test তৈরি করা হয়।
Test Environment Setup: বাস্তব পরিবেশের মতো test environment তৈরি করে smoke test চালানো হয়।
Validation কার্যক্রম
System Testing: সম্পূর্ণ system যাচাই করা হয়।
User Acceptance Testing (UAT): End-user দ্বারা system যাচাই করা হয়।
Performance ও Usability Testing: System-এর performance ও ব্যবহারযোগ্যতা নিশ্চিত করা হয়।
Test Execution ও Bug Reporting: Test চালিয়ে bug শনাক্ত ও fix যাচাই করা হয়।
Test Closure ও Reporting: Test result বিশ্লেষণ ও documentation করা হয় এবং ভবিষ্যতের উন্নয়নের জন্য আলোচনা করা হয়।
- ☆38Miscellaneous_mathMath-othersSuppose that a digitized TV picture is to be transmitted from a source that uses a matrix of 480 × 500 picture elements (pixels), where each pixel can take on one of 32 intensity values. Assume that 30 pictures are sent per second. (This digital source is roughly equivalent to broadcast TV standards that have been adopted.) Find the source rate R (bps).BB, AME, 23_math | IT Mathematical Question
Solution: Here, The source uses 480 x 500 pixels/picture And, 30 pictures are sent per second.
So, we can find the source rate in pixels/s as: \[ (30 \, \text{pictures/s}) \times (480 \times 500 \, \text{pixels/picture})\] \[= 7.2 \times 10^6 \, \text{pixels/s} \]
Now, each pixel can take on one of 32 intensity values and these 32 intensity values can be represented by: \[ \log_2 32 = \log_2 2^5 = 5 \, \text{bits} \] We can find the source rate in bits/s (bps) as:
R = \( 7.2 \times 10^6 \, \text{pixels/s} \times 5 \, \text{bits/pixel} \) \[ = 36 \times 10^6 \, \text{bps} = 36 \, \text{Mbps} \]
source:[brainly.in]
- ☆39Data StructureHashingConsider strong entries with integer keys. Suppose the hash function is h (k) = k mod 13. Insert in the given order entries with keys 10, 3, 6, 16, 17, 19 in to the hash table using linear probing to resolve collisions. Show all the work.BB, AP, 23 | Assistant Programmer
The hash function is given as h(k)=k mod 13.
The table size is 13, meaning we have indices from 0 to 12.Step-by-Step Insertion Process
Key: 10
Hash value: h(10) = 10 mod 13 = 10. Insert 10 at index 10.Key: 3
Hash value: h(3) = 3 mod 13 = 3. Insert 3 at index 3.Key: 6
Hash value: h(6) = 6 mod 13 = 6. Insert 6 at index 6.Key: 16
Hash value: h(16) = 16 mod 13 = 3. Index 3 is occupied. Use linear probing and insert 16 at index 4.Key: 17
Hash value: h(17) = 17 mod 13 = 4. Index 4 is occupied. Use linear probing and insert 17 at index 5.Key: 19
Hash value: h(19) = 19 mod 13 = 6. Index 6 is occupied. Use linear probing and insert 19 at index 7.Final Hash Table
Index Value 0 - 1 - 2 - 3 3 4 16 5 17 6 6 7 19 8 - 9 - 10 10 11 - 12 - Summary
The final hash table after inserting all keys using linear probing is as follows:[ - , - , - , 3 , 16 , 17 , 6 , 19 , - , - , 10 , - , - ]
- ☆40Computer SecurityCIAPreserving confidentiality integrity and availability of data is a restatement of the concern over falsification, interception, masquerade and denial of service. Explain how the first three concepts relate to the last four.BB, AP, 23 | Assistant Programmer
The concepts of confidentiality, integrity, and availability (CIA triad) directly address the security concerns of falsification, interception, masquerade, and denial of service.
Confidentiality ensures that sensitive information is accessible only to authorized users, protecting against interception, where data could be accessed or stolen by unauthorized parties.
Integrity guarantees that data remains accurate and unaltered, defending against falsification, which involves malicious modification of data, and masquerade, where attackers assume false identities to tamper with information.
Availability ensures that information and resources are accessible when needed, countering denial of service (DoS) attacks that aim to make systems or data unavailable to legitimate users.
By maintaining confidentiality, integrity, and availability, organizations can effectively mitigate these four major security threats and enhance overall data protection.
Confidentiality, Integrity, Availability (CIA triad)-এর ধারণাগুলো মূলত চারটি security threat-এর সাথে সম্পর্কিত: falsification, interception, masquerade, এবং denial of service।
Confidentiality (গোপনীয়তা): সংবেদনশীল তথ্যকে শুধুমাত্র authorized users-এর জন্য accessible রাখে। এটি interception থেকে রক্ষা করে, অর্থাৎ unauthorized ব্যক্তি তথ্য access বা steal করতে পারবে না.
Integrity (অখণ্ডতা): নিশ্চিত করে যে তথ্য correct এবং unaltered আছে। এটি falsification থেকে রক্ষা করে, যেখানে data maliciously modify করা হয়, এবং masquerade থেকে, যেখানে attacker false identity ব্যবহার করে information manipulate করতে পারে.
Availability (উপলব্ধতা): তথ্য এবং resources ব্যবহারকারীদের প্রয়োজন অনুযায়ী accessible রাখে। এটি denial of service (DoS) attack থেকে রক্ষা করে, যা legitimate users-এর জন্য system বা data কে unavailable করতে চায়.
সারসংক্ষেপে, maintaining the CIA triad এই চারটি security threat mitigate করতে সাহায্য করে এবং overall data protection ensure করে।
- ☆41Database Management SystemKeysSuppose that we have a relational database with the following table. Underlined one represent primary key
Movies (mid, title, year)
Write a SQL query to return the number of movies that are romantic comedies.
People (pid, name)
Genres (gid, genre)
HasRole (pid, mid, role)
Has Genre (gid, mid)BB, AP, 23 | Assistant ProgrammerSELECT COUNT(*) FROM Movies, Genres, HasGenre WHERE Movies.mid = HasGenre.mid AND HasGenre.gid = Genres.gid AND Genres.genre = "romantic comedy";
- ☆42Computer NetworkOSI/TCP-IPIn order to prevent that the company decided to add end to end encryption techniques which layer of the OSI model is suitable to work in considering parameters like development time, software maintainability and development cost, Give reasons for your concepts.BB, AP, 23 | Assistant Programmer
Suitable OSI Layer for End-to-End Encryption
To implement end-to-end encryption (E2EE) while considering development time, software maintainability, and development cost, the most suitable layer of the OSI model is the Application Layer (Layer 7).
Reasons for Choosing the Application Layer
- Faster Development Time: Encryption at the application layer can be implemented directly within the application logic. Developers do not need to modify lower-level networking protocols, which significantly reduces development time.
- Better Software Maintainability: Application-layer encryption is easier to update, debug, and maintain. Changes can be made without affecting the underlying network infrastructure or operating system.
- Lower Development Cost: No changes are required in routers, switches, or transport-layer implementations. This avoids hardware upgrades and reduces overall implementation cost.
- True End-to-End Security: Data is encrypted at the sender’s application and decrypted only at the receiver’s application. Intermediate systems (routers, proxies, servers) cannot read the data.
- Platform Independence: Application-layer encryption works across different networks, protocols, and platforms without compatibility issues.
Why Not Lower Layers?
- Transport Layer (e.g., TLS): Requires certificate management and protocol-level integration, increasing complexity and cost.
- Network/Data Link Layers: Require hardware or OS-level changes, leading to high cost and poor maintainability.
Considering development time, cost efficiency, and long-term maintainability, implementing end-to-end encryption at the Application Layer is the best and most practical choice.
End-to-End Encryption-এর জন্য উপযুক্ত OSI Layer
End-to-end encryption (E2EE) বাস্তবায়নের ক্ষেত্রে যদি development time, software maintainability এবং development cost বিবেচনা করা হয়, তাহলে OSI model-এর মধ্যে সবচেয়ে উপযুক্ত হলো Application Layer (Layer 7)।
Application Layer নির্বাচন করার কারণ
- কম Development Time: Application layer-এ encryption সরাসরি application logic-এর ভেতরে implement করা যায়। নিচের network protocol পরিবর্তনের প্রয়োজন হয় না, ফলে সময় কম লাগে।
- সহজ Software Maintainability: Application-level encryption সহজে update, debug এবং maintain করা যায়। Network বা OS পরিবর্তন ছাড়াই security update সম্ভব।
- কম Development Cost: Router, switch বা hardware পরিবর্তনের দরকার হয় না। এতে implementation cost অনেক কমে যায়।
- প্রকৃত End-to-End Security: Sender-এর application-এ data encrypt হয় এবং receiver-এর application-এই decrypt হয়। মাঝখানের কোনো system data পড়তে পারে না।
- Platform Independent: Application layer encryption বিভিন্ন network ও platform-এ একইভাবে কাজ করে।
নিচের Layer গুলো কেন উপযুক্ত নয়?
- Transport Layer (যেমন TLS): Certificate management ও protocol complexity বেশি, ফলে খরচ ও রক্ষণাবেক্ষণ কঠিন।
- Network/Data Link Layer: Hardware বা OS পরিবর্তন দরকার হয়, যা ব্যয়বহুল ও জটিল।
Development time, খরচ এবং ভবিষ্যৎ maintainability বিবেচনা করলে Application Layer-এ end-to-end encryption বাস্তবায়নই সবচেয়ে কার্যকর সমাধান।


Adjacency List Representation
Answer the following Question using the Bankers algorithm,
The diagram illustrates the process of sending an email from the sender to the receiver
The diagram represents a secure network architecture for Bangladesh Bank, where client-server communication is protected using firewalls:
[source: